

eScan releases free scanner for PHP2Shell and weak TLS certificates
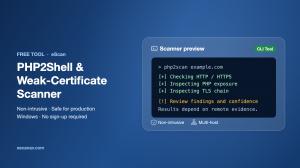
eScan has launched a free Windows command-line scanner to help organizations identify exposure to the critical PHP2Shell flaw and recoverable eMudhra/emSign TLS certificates. The tool is designed to safely scan live environments and show where patching or certificate replacement is needed.
Why it matters: - PHP2Shell and the eMudhra certificate weakness affect infrastructure that many organizations rely on for public websites and secure connections. - The new scanner gives defenders a fast way to find exposed systems before attackers can exploit them. - The tool is free, which lowers the barrier for broad checks across production estates.
What happened: - eScan (MicroWorld Technologies Inc.) released a free command-line scanner on November 2, 2026. - The scanner checks systems for exposure to PHP2Shell, the critical PHP remote-code-execution flaw tracked as CVE-2026-109618 and CVE-2026-109619. - The tool also inspects TLS certificate chains for recoverable private keys tied to eMudhra certificates issued under the emSign brand. - The scanner is available for Windows with no registration required at the scanner download page.
The details: - PHP2Shell is rated 9.8 out of 10 on the CVSS v3.1 scale. - The flaw can let an attacker run code on a server with no credentials and no user interaction. - Because the bug sits in PHP core, every site hosted on a vulnerable server can be exposed. - PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 include the fixes. - Older PHP branches receive limited or no official fixes. - Published internet-scan data showed roughly 2.6 million internet-facing services advertising a PHP version when the patch shipped. - Close to three-quarters of those services were running branches that will not receive an official release. - Attackers were already probing for the flaw before the patch was public. - Researchers later found that eight intermediate certificate authority keys run by eMudhra under emSign were generated so poorly that the private keys were tiny whole numbers. - One of the keys was the number 4. - The private keys could be recovered in under a second. - The issue is tracked as CVE-2026-111943. - Major browsers moved to withdraw trust from the affected roots. - eMudhra said it would exit the global TLS certificate business.
Between the lines: - The scanner addresses two problems that are hard to validate quickly at scale: vulnerable PHP runtimes and certificate chains that look valid but rest on weak cryptography. - The tool does not send exploit traffic, so it is designed to be safe on live production, customer and government infrastructure. - The scanner confirms vulnerable versions with high confidence, but it does not declare a host safe based on remote checks alone because distributions can patch without changing version numbers. - That cautious design matters because false reassurance can delay remediation.
What's next: - Organizations can use the scanner to identify vulnerable hosts, check certificate chains and prioritize remediation. - The tool can scan an IP address, a network range, a domain or a file of targets. - Given a domain and the relevant option, the scanner can also discover subdomains through Certificate Transparency records and scan those hosts too. - The scanner prints a verdict, supporting evidence and the recommended remediation for each finding.
The bottom line: - eScan is betting that defenders need fast, safe and free visibility into both software exposure and certificate trust before attackers exploit either weakness.
Disclaimer: This article was produced by AGP Wire with the assistance of artificial intelligence based on original source content and has been refined to improve clarity, structure, and readability. This content is provided on an “as is” basis. While care has been taken in its preparation, it may contain inaccuracies or omissions, and readers should consult the original source and independently verify key information where appropriate. This content is for informational purposes only and does not constitute legal, financial, investment, or other professional advice.
Sign up for:
Advertising Press Releases
The daily local news briefing you can trust. Every day. Subscribe now.
Check Your Email!
We sent a one-time activation link to: .
Confirm it's you by clicking the email link.
If the email is not in your inbox, check spam or try again.
Welcome back!
is already signed up. Check your inbox for updates.